No safety without security.
Connected products are under compliance pressure. We know your requirements.
We know which laws and standards apply to your connected product before you even ask. Our security experts take the regulatory complexity off your hands: from CRA, NIS-2, MDR and RED through the Machinery Regulation and UNECE R155/R156 to IEC 62443, EN 18031 and ISO/SAE 21434. They place your case, translate the requirements into a clear development path and guide you from the maturity analysis all the way to monitoring in the field.
- CRA
- NIS-2
- MDR
- RED
- Machinery Regulation
- UNECE R155 / R156
- IEC 62443
- ISO/SAE 21434
- IEC 81001-5-1
- EN 18031
- TS 50701
The time is up...
The Cyber Resilience Act is binding for manufacturers, importers and distributors of products with digital elements on the EU market. NewTec supports you as a partner in putting it into practice: from the maturity and gap analysis through compliant security product development to safe operation in the field.
Cyber resilience starts before development.
Security engineering covers everything, from development processes and competence management through system design to decommissioning.
Enabling: processes & competencies
Maturity assessment and gap analysis, introduction of legally and standard-compliant processes (e.g. CRA), coaching of the development team across all relevant aspects of security engineering.
Learn more
Security product development
Electronics and software development to the V-model: product classification under the CRA, risk analyses (TARA, IRA, DRA), documentation. Pre-qualified solution building blocks speed up development.
Learn more
Safe operation, free for the future.
Managed services across the entire lifecycle: vulnerability monitoring & penetration testing, Product Incident Response Team (PSIRT), PKI management: cyber resilience even after market launch.
Learn more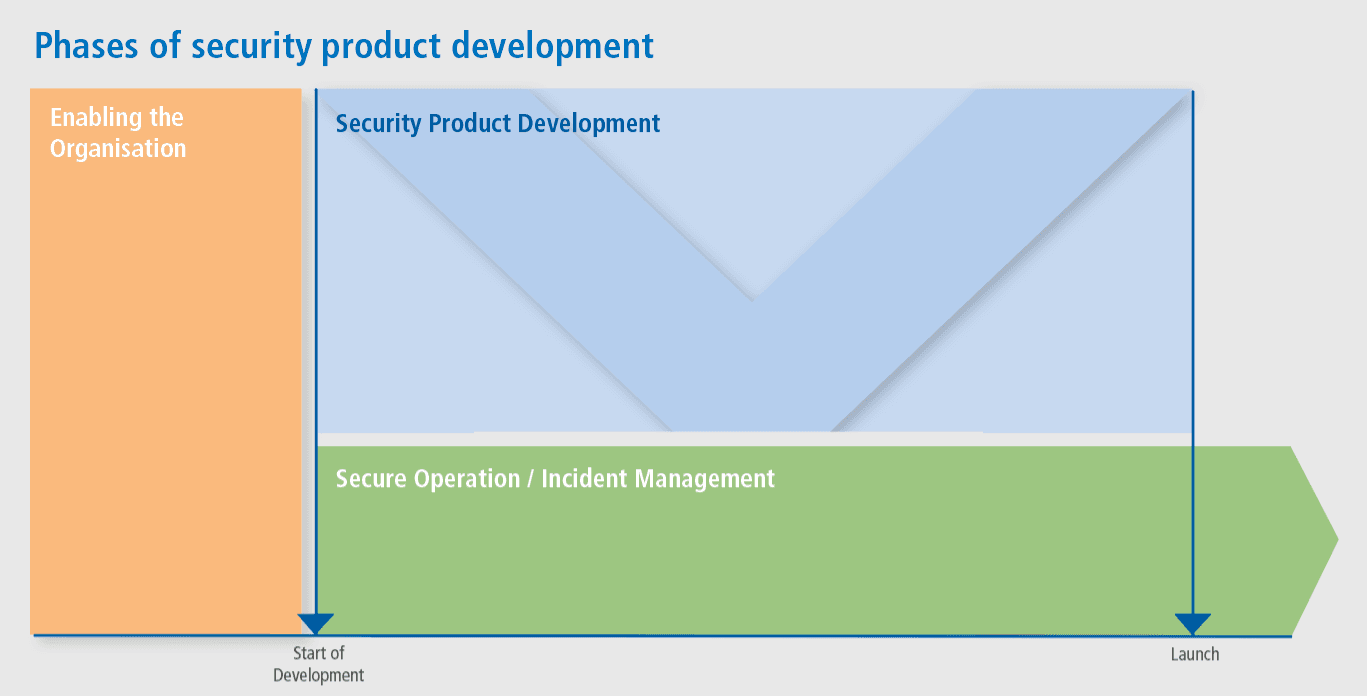
Three pillars of security engineering
Security engineering does not begin with the development of a product, nor does it end with its market launch. Comprehensive cyber resilience requires everything to be taken into account, from development processes, competence management and system design through secure operation to decommissioning.
We distinguish between three overarching pillars of security engineering:
The first pillar is about enabling the organisation. The aim is to implement processes that comply with laws and standards and to equip the development team with the skills they need to develop cyber-secure products.
The second pillar covers classic product development according to the V-model with a design phase, implementation phase, and testing and validation phase.
The third pillar is about ensuring secure operation.
Cybersecurity is a must!
A few clicks to your security training!
Regulations such as the Cyber Resilience Act (CRA), NIS2 or IEC 62443 explicitly require proof of qualified specialists. Sometimes the fastest lever is not a service package but targeted training, so your team keeps the topic in house.
At the NewTec Academy we bundle our knowledge into open and in-house formats: compact, hands-on and with trainers drawn from live projects.
- ✓Secure implementation practices for software and hardware
- ✓Security basics for engineers: security by design in the engineering process
- ✓TARA method training: getting risk analysis under CRA, MDR & co. right
Security product development with NewTec.
From cybersecurity management through threat and risk analyses to secure implementation, verification and hands-on guidelines, we guide your product development holistically, in a structured way and in line with the standards.
Secure product development under the CRA, compliant with IEC 62443 (4-1/4-2) and EN 18031. From TARA and security requirements to robust proof via the NewTec IT security attestation.
Modular work packages, from TARA through security requirements engineering, security concept and security development to security testing and assessment. You choose what your project really needs.
Pre-qualified solution building blocks, platforms and infrastructure cut effort and cost, for a shorter time to market without compromising on security.
PSIRT as a Managed Service.
Our PSIRT service supports you in responding to reported security incidents and vulnerabilities in your products in a structured and fast way, across the entire product lifecycle.
We take care of monitoring, analysis and assessment as well as the coordination and communication of the appropriate measures. That way you not only meet regulatory requirements but also strengthen your customers’ trust in the security of your products.
- ✓Monitoring, analysis and assessment of reported incidents
- ✓Coordination and communication of the response
- ✓Various SLAs: from basic monitoring to prioritised response
- ✓Meeting regulatory requirements (CRA, NIS2, IEC 62443)
Independent proof of security and compliance.
With requirements such as the Cyber Resilience Act or specifications from EU notified bodies, traceable security assessments are becoming more important. NewTec carries out structured penetration tests & assessments to international standards.
The result is the NewTec IT security attestation: independent proof of the technical security of your product. A strong argument for approvals, customer requirements and audits, and towards supervisory authorities such as the FDA or EU notified bodies.
- ✓IEC 62443: industrial cybersecurity
- ✓ISO/SAE 21434: automotive cybersecurity
- ✓IEC 81001-5-1: health software security
PKI management and hosting.
We offer a powerful toolchain for the central management of a product-related Public Key Infrastructure (PKI), designed for the demands of industrial and connected products. You benefit from secure certificate management, digital device identity and encrypted communication, compliant with IEC 62443, EN 18031, CRA and NIS2. Our solution meets the core requirements of current standards and laws. It helps you prove the authenticity, integrity and trustworthiness of your products in an audit-ready way, with no infrastructure or operational overhead of your own.
With our offering you create the foundation for secure communication, software authenticity and regulatory compliance: ready to run, scalable and future-proof.
- ✓Provision & operation of a complete X.509 certificate infrastructure (Root CA, OCSP, CRL)
- ✓Certificate management toolchain for issuance, renewal and revocation
- ✓Multi-tenant solution, hosted in KRITIS-compliant data centres in Germany
- ✓Technical & organisational integration into OT and product environments
- ✓Optional: integration with IAM/security platforms (e.g. access control, signature verification)
Our customer projects in the security space
Go deeper on the topic. Articles from our knowledge hub.
Let’s talk about your security project.
We place your use case in line with the standards, determine the maturity of your processes and show the fastest route to cyber-resilient products.