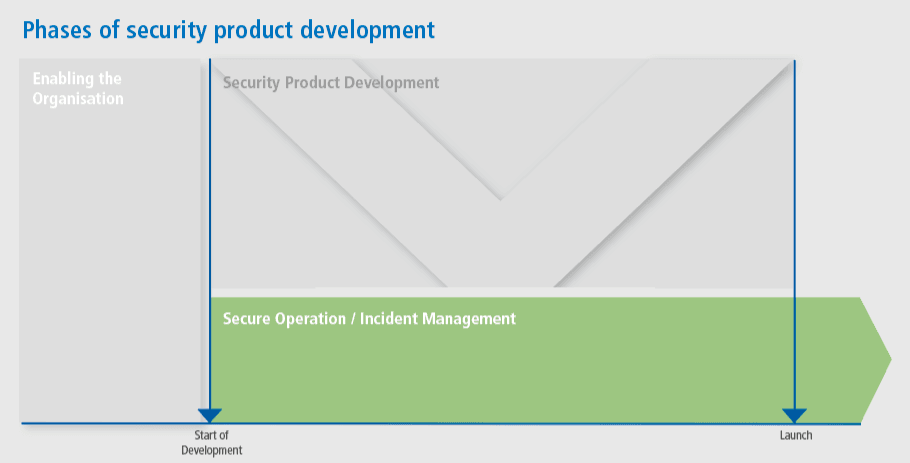
Secure operation throughout the entire lifecycle
Cybersecurity does not end with a product's market launch. NewTec takes care of securing and monitoring your systems for you through automated vulnerability monitoring and effective vulnerability management. We also optimise your update management to close security gaps at an early stage.
In addition, we provide a public key infrastructure (PKI) to enable secure communication and authentication. To ensure the availability of security-related system components throughout the entire product lifecycle, we are also happy to take care of obsolescence management.
Our services at a glance
Product Security Incident Response (PSIRT) as a managed service.
With our IT security attestation, you receive independent proof of security and compliance.
At NewTec Academy, we bring our knowledge together in open and in-house formats – concise, practical and delivered by trainers from ongoing projects.
We provide a powerful toolchain for the central management of a product-specific public key infrastructure (PKI).
PSIRT as a Managed Service.
Our PSIRT service supports you in responding to reported security incidents and vulnerabilities in your products in a structured and fast way, across the entire product lifecycle.
We take care of monitoring, analysis and assessment as well as the coordination and communication of the appropriate measures. That way you not only meet regulatory requirements but also strengthen your customers’ trust in the security of your products.
- ✓Monitoring, analysis and assessment of reported incidents
- ✓Coordination and communication of the response
- ✓Various SLAs: from basic monitoring to prioritised response
- ✓Meeting regulatory requirements (CRA, NIS2, IEC 62443)
Independent proof of security and compliance.
With requirements such as the Cyber Resilience Act or specifications from EU notified bodies, traceable security assessments are becoming more important. NewTec carries out structured penetration tests & assessments to international standards.
The result is the NewTec IT security attestation: independent proof of the technical security of your product. A strong argument for approvals, customer requirements and audits, and towards supervisory authorities such as the FDA or EU notified bodies.
- ✓IEC 62443: industrial cybersecurity
- ✓ISO/SAE 21434 — Automotive Cybersecurity
- ✓IEC 81001-5-1 — Health-Software-Security
A few clicks to your security training!
Regulations such as the Cyber Resilience Act (CRA), NIS2 or IEC 62443 explicitly require proof of qualified specialists. Sometimes the fastest lever is not a service package but targeted training, so your team keeps the topic in house.
At the NewTec Academy we bundle our knowledge into open and in-house formats: compact, hands-on and with trainers drawn from live projects.
- ✓Secure Implementation Practices für Software und Hardware
- ✓Security basics for engineers: security by design in the engineering process
- ✓TARA method training: getting risk analysis under CRA, MDR & co. right
PKI management and hosting.
We offer a powerful toolchain for the central management of a product-related Public Key Infrastructure (PKI), designed for the demands of industrial and connected products. You benefit from secure certificate management, digital device identity and encrypted communication, compliant with IEC 62443, EN 18031, CRA and NIS2. Our solution meets the core requirements of current standards and laws. It helps you prove the authenticity, integrity and trustworthiness of your products in an audit-ready way, with no infrastructure or operational overhead of your own.
With our offering you create the foundation for secure communication, software authenticity and regulatory compliance: ready to run, scalable and future-proof.
- ✓Provision & operation of a complete X.509 certificate infrastructure (Root CA, OCSP, CRL)
- ✓Certificate management toolchain for issuance, renewal and revocation
- ✓Multi-tenant solution, hosted in KRITIS-compliant data centres in Germany
- ✓Technical & organisational integration into OT and product environments
- ✓Optional: integration with IAM/security platforms (e.g. access control, signature verification)
Let’s talk about your security project.
We place your use case in line with the standards, determine the maturity of your processes and show the fastest route to cyber-resilient products.