Equipped with robust processes and expertise for the CRA, NIS 2 and more
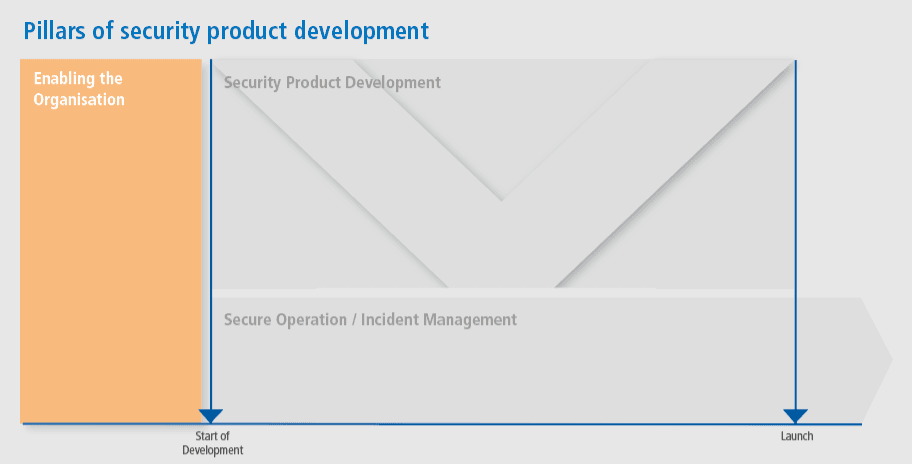
To develop and operate cyber-secure machines and systems, manufacturers must design their processes in line with legal requirements. These include the Cyber Resilience Act (CRA), which – depending on the product – requires proof of conformity by self-declaration or certification.
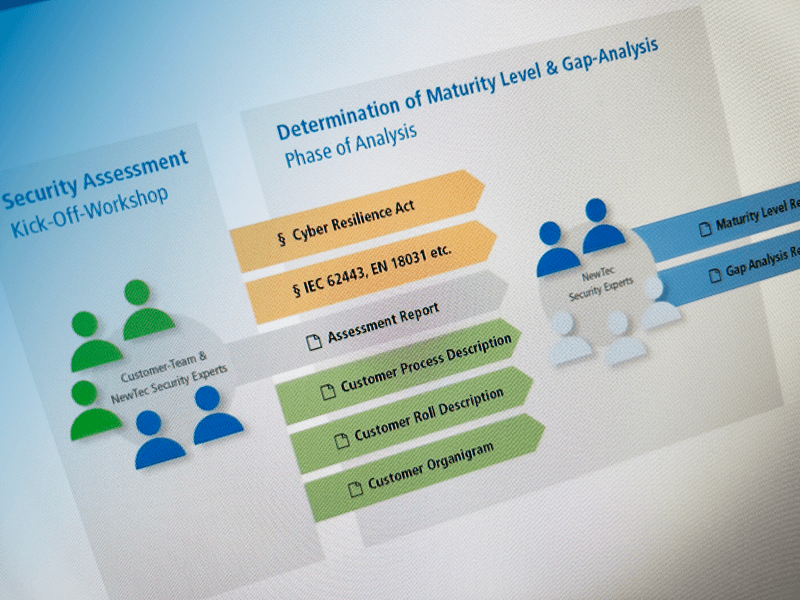
With our security services, we support manufacturers across all industries in introducing and optimising security development processes. After determining your company’s maturity level by means of a gap analysis, we propose concrete measures and accompany the introduction of legally compliant processes. We also prepare the necessary documentation and strengthen security expertise within your company through workshops, training courses and seminars.
- Cyber Resilience Act (CRA)
- NIS 2 Directive for critical infrastructure or industry-specific regulations
- Medical Device Regulation (MDR)
- Radio Equipment Directive (RED)
- Machinery Regulation
- UNECE R 155 and R 156
- Industry-specific requirements (FDA, NIST, BSI, NSH, ...)
- and others
We equip your company for the relevant requirements.
How can we help enable your company with legally compliant processes and certified employee competencies?
Let’s talk about your security project.
We place your use case in line with the standards, determine the maturity of your processes and show the fastest route to cyber-resilient products.