How robust are your development and support processes?
Do your existing development and support processes meet the requirements of the Cyber Resilience Act (CRA) and relevant standards such as IEC 62443-4-1, EN 18031, etc.?
The maturity assessment shows you which requirements are relevant for meeting the standard that applies to you, where your company currently stands and which steps are still necessary. You receive a prioritised to-do list that enables structured project planning for introducing standard-compliant processes. The result can also provide documented evidence of compliance with the standard. This evidence of your cybersecurity competence serves auditors and assessors as a basis for certification.
Know where you stand, set your course: your roadmap to CRA compliance
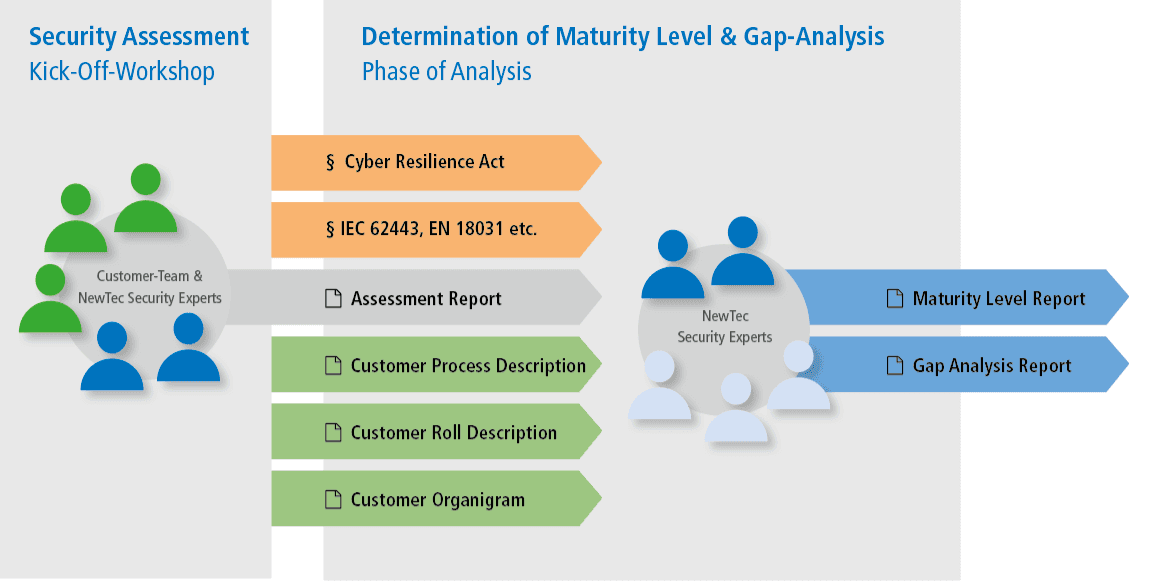
The maturity assessment and gap analysis show how well your existing development and support processes already meet the requirements of the Cyber Resilience Act (CRA) and relevant standards such as IEC 62443-4-1, EN 18031, etc. They identify gaps in a targeted way and prioritise concrete measures to make your processes compliant with the standards.
The result is presented in our Maturity Level Report – with clear references to the specific requirements of the respective security standard. These reports enable fast, standard-compliant implementation of the requirements and at the same time serve as evidence of compliance. This gives you a practical roadmap that reduces development costs, improves your chances of certification and strengthens security expertise within your company over the long term.
We support you in two steps
In a two-day workshop at your premises, our cybersecurity experts lay the foundations for the process gap analysis in accordance with the CRA. Based on the workshop results, we then carry out a detailed analysis within four weeks. Do you have any questions or would you like a quote? Please feel free to contact us.

Let’s talk about your security project.
We place your use case in line with the standards, determine the maturity of your processes and show the fastest route to cyber-resilient products.